Define what reliable evidence means for the task
Before relying on a record, identify its intended use and the evidence needed for that decision. A record can be easy to retrieve and still contain an incorrect identifier or an unsupported result. Conversely, an old record may be valid historical evidence even though the procedure has since changed. Assess context as well as recency.
NIST's data-integrity glossary includes definitions concerned with unauthorized alteration and accidental change or loss. Those definitions have source-specific security contexts. Protection against change does not itself prove that an original entry was accurate. The checks below are a proposed quality-record review workflow, not a comprehensive security or regulatory control framework.
Check the evidence before acting
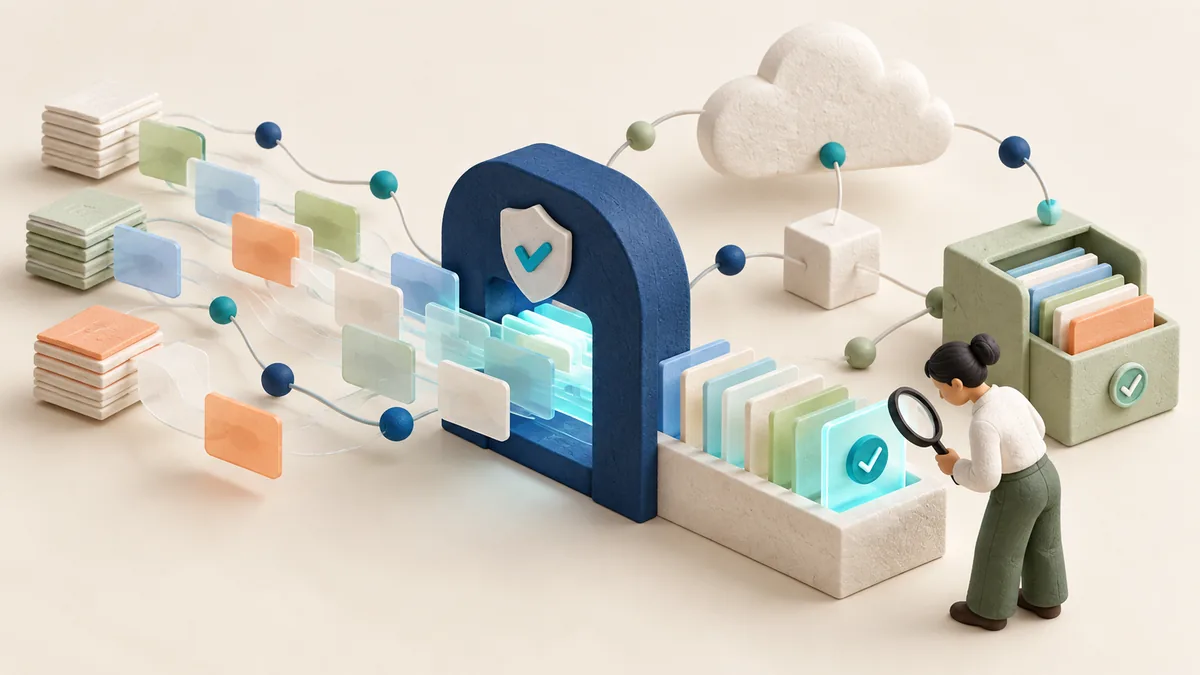
- Identify the record, activity, relevant date and responsible person.
- Compare important entries with the available source evidence.
- Check units, identifiers, scope and the instruction relevant to the work.
- Record missing information and distinguish it from confirmed errors.
- Decide who can resolve the question and whether the result can be used meanwhile.
Choose review depth according to the decision and applicable requirements. This article proposes no universal sample size, scoring method or rule that every discrepancy is a nonconformity. If a requirement needs interpretation, assign it for qualified review before making a conformity conclusion.
Correct with context and follow-up
Illustrative workflow: a reviewer finds two different equipment identifiers in a sample check record. The owner examines the original source, determines which entry needs correction and follows the organization's approved change procedure. The team records the reason, relevant authorization and any effect on decisions already made. It then verifies the correction and considers whether the same issue occurs elsewhere.
Confirm how your current system presents correction history and access permissions. Do not silently replace uncertain information with a guess or assume that a visible log explains every event. Decide which evidence must be retained and who approves the disposition using the applicable process.
Measure the work without inventing savings
Track review time, unresolved questions and repeated discrepancies for a defined period and process. Use a comparable baseline when evaluating a change. Separate measured expenditure from recovered staff capacity and estimated avoided problems. A reduced count may reflect changed reporting or workload, so record those limits before attributing improvement to software.
Evaluate controls and maintain ownership
Use the document and record review guide to separate instruction controls from completed evidence. In a demonstration, try the relevant review and correction tasks with suitable sample data. Confirm what is visible to each role, what needs configuration and what the workflow does when evidence is incomplete.
The QMS software evaluation guide helps capture those results. Software can structure collection and follow-up, while people remain responsible for evidence, interpretation and review. An enabled feature does not establish that accuracy is automatic or that all records are continually verified.
Reference checked 7 October 2026: NIST's source-specific glossary above. No Qlutch security certification, automatic validation, customer saving or detailed regulatory interpretation is asserted.